

1. 簡介
本程式碼實驗室將說明如何在 Google Compute Engine (GCE) 虛擬機器 (VM) 上部署 AlloyDB Omni 高可用性 (HA) 叢集。完成本程式碼研究室後,您將佈建高可用性參考架構,其中包含 3 個資料庫節點和 2 個 HAProxy 節點,以及用於管理作業的控制節點。
必要條件
- 從 Cloud 控制台存取 Google Cloud 專案和 Cloud Shell。
- 已安裝並設定 Google Cloud SDK (
gcloud)。如要瞭解如何安裝 gcloud,請參閱 gcloud-install - 已安裝 Terraform v1.9.8。
課程內容
- 如何建立及準備 GCE VM,以供 AlloyDB Omni 使用。
- 如何安裝及執行 AlloyDB Omni RPM 自動調度管理工具。
- 如何為高可用性參考架構安裝及設定 AlloyDB Omni RPM。
軟硬體需求
- 取得 AlloyDB Omni RPM 和 RPM 自動調度管理工具的網址連結。如要申請,請填寫 AlloyDB Omni 註冊表單。連結會傳送至您的電子郵件,也就是存放區網址伺服器。初始化下列環境變數,方便您在程式碼研究室中使用網址。
export ORCHESTRATOR_ANSIBLE_COLLECTION_PATH="..." export ALLOYDB_OMNI_REPOSITORY_URL="..." export ALLOYDB_OMNI_ORCHESTRATOR_REPOSITORY_URL="..." export ALLOYDB_OMNI_COMMON_REPOSITORY_URL="..." export ETCD_REPOSITORY_URL="..." - 可存取 AlloyDB Omni 部署堆疊的終端機。您可以使用 Cloud Shell 達成此目的。
2. 設定和需求條件
專案設定
建立 Google Cloud 專案
- 在 Google Cloud 控制台的專案選擇器頁面中,選取或建立 Google Cloud 專案。
- 確認 Cloud 專案已啟用計費功能。瞭解如何檢查專案是否已啟用計費功能。
啟動 Cloud Shell
雖然可以透過筆電遠端操作 Google Cloud,但在本程式碼實驗室中,您將使用 Google Cloud Shell,這是可在雲端執行的指令列環境。
在 Google Cloud 控制台中,點選右上角工具列的 Cloud Shell 圖示:
你也可以依序按下 G 和 S 鍵。如果您位於 Google Cloud 控制台,或使用這個連結,這個序列會啟用 Cloud Shell。
佈建並連線至環境的作業需要一些時間才能完成。完成後,您應該會看到類似下方的內容:
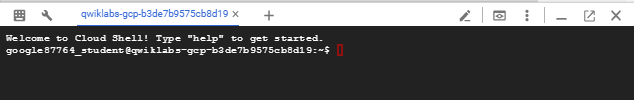
這個虛擬機器已預先安裝所有必要的開發人員工具,並提供永久的 5 GB 主目錄,而且可在 Google Cloud 運作,大幅提升網路效能並強化驗證功能。您可以在瀏覽器中完成本程式碼研究室的所有作業。你不需要安裝任何軟體。
3. 建立 Google Cloud Compute Engine 虛擬機器
準備 Terraform 指令碼
- 為專案 ID 和所需叢集名稱定義環境變數。您會在整個程式碼研究室中使用這些功能。
export PROJECT="your-project-id" export CLUSTER="your-cluster-name" - 確認您已登入 Google Cloud 帳戶使用者。
gcloud auth login - 為部署作業建立目前使用的目錄,並從存放區來源複製必要的 Terraform 設定檔。
mkdir -p ~/alloydb-omni/$PROJECT/$CLUSTER cd ~/alloydb-omni/$PROJECT/$CLUSTER gcloud storage cp gs://alloydb-omni-install/rpm-orchestrator/gce/terraform/*.tf . - 建立
terraform.tfvars檔案,根據參考架構指定必要參數,如下所示:cat > terraform.tfvars <<EOF # Required instance counts for reference architecture db_instance_count = 3 haproxy_instance_count = 2 control_instance_count = 1 # Optional: Customize if needed with the below variables # os_image = "rocky-linux-cloud/rocky-linux-9" # zone = "us-west4-c" # region_1 = "us-west4" # db_instance_type = "c4-highmem-4" # db_disk_type = "hyperdisk-balanced" # db_data_size = "50" # GB # data_dir = "/data" EOF
執行 Terraform 指令碼並驗證
- 您現在可以佈建 VM。
terraform init - 建立 VM 前,請確認您有建立 VM 和其他資源的必要存取權。總而言之,您需要下列權限。
roles/compute.admin roles/iam.roleAdmin roles/compute.osAdminLogin roles/iam.serviceAccountCreator roles/iam.serviceAccountUser roles/artifactregistry.repoAdmin roles/storage.objectUser roles/resourcemanager.projectIamAdmin roles/serviceusage.serviceUsageAdmin - 驗證設定,然後套用設定來佈建資源。
terraform validate terraform apply --auto-approve - Terraform 完成後,請使用
gcloud列出已建立的執行個體,確認虛擬機器已成功建立。gcloud compute instances list --filter="name~$CLUSTER" --project=$PROJECTexport ZONE=$(gcloud compute instances list \ --filter="name=$CLUSTER-control" \ --format="value(zone)" --project=$PROJECT)
4. 準備要部署的 VM
您需要建立控制節點的 SSH 工作階段,並執行步驟,啟用所有 VM (也稱為節點) 的 SSH 存取權。
- 確認專案和叢集的環境變數已定義。
export PROJECT="your-project-id" export CLUSTER="your-cluster-name" - 建立安全殼層金鑰,並新增該金鑰以登入控制項 VM。
# Replace values with your specific GCP project, cluster and zone details ssh-keygen -t ed25519 -f $HOME/.ssh/google_compute_engine gcloud compute os-login ssh-keys add --key-file=$HOME/.ssh/google_compute_engine.pub --project=$PROJECT - 建立防火牆規則,允許 SSH 連線和 VRRP 流量。
gcloud compute config-ssh --project=$PROJECT gcloud compute firewall-rules create $CLUSTER-allow-ssh --network=$CLUSTER --project=$PROJECT --direction=INGRESS --action=allow --rules=tcp:22 --source-ranges="0.0.0.0/0" gcloud compute firewall-rules create $CLUSTER-allow-vrrp --network=$CLUSTER --project=$PROJECT --allow=112 --source-ranges="0.0.0.0/0" - 透過 SSH 連線至控制項 VM:
gcloud compute ssh "$CLUSTER-control" --zone=$ZONE --project=$PROJECT - 在控制節點上建立 Linux 群組,名稱與使用者名稱相同:
sudo groupadd -f $(id -un) sudo usermod -aG $(id -un) $(id -un) - Terraform 設定會建立幾個設定指令碼,並在控制 VM 的
/tmp/目錄中暫存這些指令碼,包括叢集名稱、服務帳戶、專案名稱等。使用控制節點上的設定指令碼,從控制節點建立無密碼的 SSH 存取權,連線至所有叢集節點。/tmp/setup-ssh-for-cluster.sh - 在本程式碼實驗室中,我們可以停用所有節點的 SELinux。Terraform 指令碼會新增「/tmp/run-all.sh」,可用於此目的。
/tmp/run-all.sh sudo setenforce 0 - 如果您已註冊 AlloyDB Omni 並取得連結,現在也該將這些網址新增至環境變數。
cat >> ~/.codelab.env <<EOF export ORCHESTRATOR_ANSIBLE_COLLECTION_PATH="..." export ALLOYDB_OMNI_REPOSITORY_URL="..." export ALLOYDB_OMNI_ORCHESTRATOR_REPOSITORY_URL="..." export ALLOYDB_OMNI_COMMON_REPOSITORY_URL="..." export ETCD_REPOSITORY_URL="..." EOFterraform/variables.tf檔案的 cidr_range 輸入變數中,為環境決定虛擬 IP,確保該 IP 不會與其他節點衝突,如下列範例所示:cat >> ~/.codelab.env <<EOF export VIRTUAL_IP="10.1.0.50" EOF
5. 在所有 VM 上安裝必要的軟體元件
下一步是在 VM 上安裝必要的軟體元件。這項作業可以在控制節點上協調。下列所有指令都必須在控制節點上執行。
- 透過 SSH 連線至控制項 VM (如果尚未連線至控制項節點)。
gcloud compute ssh "$CLUSTER-control" --zone=$ZONE --project=$PROJECTsource ~/.codelab.env - 在控制節點上,安裝 Ansible 和必要的 Python 程式庫。
sudo dnf install -y https://dl.fedoraproject.org/pub/epel/epel-release-latest-9.noarch.rpm -y sudo dnf install -y ansible sudo dnf install -y python3-grpcio python3-protobuf python3-googleapis-common-protos python3-grpcio-status - 接著,下載 RPM Orchestrator Ansible 集合 tar 檔案,並安裝該檔案。
gcloud storage cp "gs://${ORCHESTRATOR_ANSIBLE_COLLECTION_PATH#https://storage.googleapis.com/}google-alloydbomni_orchestrator-*.tar.gz" .
COLLECTION_FILE=$(ls -1 google-alloydbomni_orchestrator-*.tar.gz \
  | sort -V | tail -n 1)
ansible-galaxy collection install "$COLLECTION_FILE"
ansible-galaxy collection list | grep alloydbomni_orchestrator
sort -V和tail -n 1指令會選取最新版本的檔案。注意:請確保 ORCHESTRATOR_ANSIBLE_COLLECTION_PATH 變數結尾有「/」。 - 自動調度管理工具會使用 Ansible 目錄格式的 Deployment 規格檔案,瞭解叢集拓撲。在控制節點上建立名為 deployment_spec.yaml 的檔案,並填入節點詳細資料。
cat > deployment_spec.yaml <<EOF alloydbomni: vars: cluster_manager: name: "$CLUSTER" etcd: setup: true config_forcewrite: true alloydbomni: major_version: "18" repo_url: $ALLOYDB_OMNI_REPOSITORY_URL alloydbomni_monitor: repo_url: $ALLOYDB_OMNI_COMMON_REPOSITORY_URL alloydbomni_cluster_manager: repo_url: $ALLOYDB_OMNI_ORCHESTRATOR_REPOSITORY_URL alloydbomni_node_manager: repo_url: $ALLOYDB_OMNI_ORCHESTRATOR_REPOSITORY_URL pgbouncer: repo_url: $ALLOYDB_OMNI_COMMON_REPOSITORY_URL pgbackrest: repo_url: $ALLOYDB_OMNI_COMMON_REPOSITORY_URL children: primary_instance_nodes: hosts: $CLUSTER-db1: $CLUSTER-db2: $CLUSTER-db3: load_balancer_nodes: hosts: $CLUSTER-haproxy1: $CLUSTER-haproxy2: EOF - 建立名為 install.yaml 的劇本,參照協調器集合中的安裝角色。
cat > install.yaml <<EOF - name: Install AlloyDB Omni cluster components hosts: all vars: ansible_become: true ansible_user: $SSH_USER ansible_ssh_private_key_file: $HOME/ssh-key-cluster-sa roles: - role: google.alloydbomni_orchestrator.install EOF - 使用廣告空間檔案執行劇本,在所有指定節點中下載並安裝 RPM。
ansible-playbook -i deployment_spec.yaml install.yaml
6. 啟動 AlloyDB Omni 叢集
在這個階段,我們已在所有節點上安裝所有必要元件。我們已準備好啟動 AlloyDB Omni 叢集。
- 透過 SSH 連線至控制項 VM (如果尚未連線至控制項節點)。
gcloud compute ssh "$CLUSTER-control" --zone=$ZONE --project=$PROJECTsource ~/.codelab.env - 產生密碼的雜湊值,並擷取已安裝的 AlloyDB Omni 資料庫版本:
encoded_password=$(echo -n "your unique password" | base64) DB_VERSION=$(/tmp/run-all.sh -t db 'rpm -q --qf "%{VERSION}\n" alloydbomni18' | tail -n 1) echo "$DB_VERSION" - 如要建立叢集,AlloyDB Omni 必須知道如何設定。建立資料庫叢集規格的檔案名稱 dbcluster.yaml。
cat > dbcluster.yaml <<EOF Secret: metadata: name: db-pw-$CLUSTER spec: type: Opaque data: $CLUSTER: $encoded_password --- DBCluster: metadata: name: $CLUSTER spec: databaseVersion: $DB_VERSION mode: "" availability: numberOfStandbys: 2 enableAutoFailover: true enableAutoHeal: true autoFailoverTriggerThreshold: 2 autoHealTriggerThreshold: 2 healthcheckPeriodSeconds: 5 replayReplicationSlotsOnStandbys: false primarySpec: adminUser: passwordRef: name: db-pw-$CLUSTER resources: cpu: 4 memory: 32Gi disks: - name: DataDisk path: $PGDATA dbLoadBalancerOptions: gcp: loadBalancerIP: "$VIRTUAL_IP" loadBalancerType: "internal" loadBalancerInterface: "eth0" EOF - 建立名為 bootstrap.yaml 的劇本,該劇本會參照啟動 Ansible 角色,建立 AlloyDB Omni 叢集。
cat > bootstrap.yaml <<EOF - name: Create DBCluster hosts: localhost roles: - role: google.alloydbomni_orchestrator.bootstrap EOF - 執行教戰手冊來建立叢集
ansible-playbook bootstrap.yaml -i deployment_spec.yaml -e resource_spec=dbcluster.yaml
7. (選用) 設定 PgBouncer 連線集區
AlloyDB Omni 支援使用 PgBouncer 的輕量型連線集區。叢集佈建完成後,您可以立即設定並啟動 PgBouncer。
- 建立名為 pgbouncer.yaml 的資源規格檔案,將連線集區與資料庫叢集建立關聯:
cat > pgbouncer.yaml <<EOF PgBouncer: metadata: name: pgbouncer-pooler spec: dbclusterRef: $CLUSTER allowSuperUserAccess: true accessMode: "rw" port: 6432 EOF - 使用先前建立的相同 bootstrap.yaml 劇本,啟動 PgBouncer 集區,並傳遞新的規格檔案:
ansible-playbook bootstrap.yaml -i deployment_spec.yaml -e resource_spec=pgbouncer.yaml
8. 驗證 AlloyDB Omni 叢集
如要確認叢集是否正常運作,以及是否可透過負載平衡器存取,您可以從控制節點使用標準 PostgreSQL 用戶端連線至叢集。
- 在控制節點上安裝 PostgreSQL 18 用戶端存放區和套件:
sudo dnf install -y https://download.postgresql.org/pub/repos/yum/reporpms/EL-9-x86_64/pgdg-redhat-repo-latest.noarch.rpm sudo dnf install -y postgresql18 - 使用先前保留的虛擬 IP 連線至叢集。系統會提示您輸入在 dbcluster.yaml 中編碼的密碼:
/usr/pgsql-18/bin/psql -h $VIRTUAL_IP -U postgres -W - 連線後,您可以執行基本 SQL 查詢來驗證叢集狀態,例如檢查資料庫版本:
postgres=# SELECT version();\q即可退出提示。
9. (選用) 使用 pgBackRest 備份資料
AlloyDB Omni 會整合 pgBackRest,直接將備份作業管理至 Cloud Storage。您可以設定備份方案,並觸發隨選備份作業,將資料備份到 Terraform 設定建立的 GCS 值區。
- 建立名為 backup_plan.yaml 的備份方案規格檔案,指向您佈建的 GCS bucket:
cat > backup_plan.yaml <<EOF BackupPlan: metadata: name: pgb-plan spec: dbclusterRef: $CLUSTER backupLocation: type: GCS gcsOptions: bucket: $CLUSTER-gcs-backups key: /backups EOF - 建立名為 backup.yaml 的 Ansible Playbook,其中會參照備份管理角色:
cat > backup.yaml <<EOF - name: Manage AlloyDB Omni Backups hosts: localhost roles: - role: google.alloydbomni_orchestrator.backup EOF - 使用 backup.yaml 劇本套用備份方案:
ansible-playbook backup.yaml -i deployment_spec.yaml -e resource_spec=backup_plan.yaml - 方案建立完成後,請建立名為 create_backup.yaml 的隨選備份資源檔案。
cat > create_backup.yaml <<EOF Backup: metadata: name: on-demand-backup spec: backupPlanRef: pgb-plan dbclusterRef: $CLUSTER EOF - 執行教戰手冊,啟動備份:
ansible-playbook backup.yaml -i deployment_spec.yaml -e resource_spec=create_backup.yaml - 如要驗證備份狀態,請建立 status.yaml 劇本:
cat > status.yaml <<EOF
- name: Fetch AlloyDB Omni Resource Status
  hosts: localhost
  roles:
    - role: google.alloydbomni_orchestrator.status
EOF
- 執行應對手冊,列出所有備份:
ansible-playbook status.yaml -i deployment_spec.yaml -e resource_type=Backup
- 或者,如要取得先前建立的特定備份詳細資訊,請傳遞
-e resource_name=on-demand-backup:
ansible-playbook status.yaml -i deployment_spec.yaml \
  -e resource_type=Backup \
  -e resource_name=on-demand-backup
10. 清除資源
部署完成後,您可以銷毀佈建的資源,以免產生費用。
- 建立名為 teardown.yaml 的應對手冊:
cat > teardown.yaml <<EOF - name: Tear down AlloyDB Omni cluster hosts: localhost roles: - role: google.alloydbomni_orchestrator.delete EOF - 使用 ansible-playbook 執行應對手冊。如果您已設定備份,請先刪除 Backup 和 BackupPlan 資源:
ansible-playbook teardown.yaml -i deployment_spec.yaml -e "resource_type=Backup" -e "resource_name=on-demand-backup" ansible-playbook teardown.yaml -i deployment_spec.yaml -e "resource_type=BackupPlan" -e "resource_name=pgb-plan"ansible-playbook teardown.yaml -i deployment_spec.yaml -e "resource_type=PgBouncer" -e "resource_name=pgbouncer-pooler"ansible-playbook teardown.yaml -i deployment_spec.yaml -e "resource_type=DBCluster" -e "resource_name=$CLUSTER" - 刪除叢集後,請登出控制節點,切換回終端機並前往 Terraform 目前使用的目錄。
注意:如果您剛登入 Cloud Shell,請記得設定下列項目:export PROJECT="your-project-id" export CLUSTER="your-cluster-name" - 刪除 VRRP 防火牆規則,並刪除 Terraform 管理的資源:
gcloud compute firewall-rules delete -q "$CLUSTER-allow-vrrp" --project="$PROJECT" gcloud compute firewall-rules delete -q "$CLUSTER-allow-ssh" --project="$PROJECT" terraform destroy - 系統提示時,請確認要銷毀裝置。由於網路資源或路徑可能殘留,有時會導致無法完全拆除,請執行下列安全清除指令,確保所有相關聯的防火牆規則、NAT 閘道、路由器、路徑、子網路和網路都已完全移除。將
REGION替換成具體的部署區域,例如「us-central1」:# Delete any remaining firewall rules associated with the cluster gcloud compute firewall-rules list --project=$PROJECT 2> /dev/null | grep ^$CLUSTER- | cut -f1 -d' ' | \ while read rule; do gcloud compute firewall-rules delete --project=$PROJECT --quiet $rule; done # Delete the Cloud NAT gateway and router if they still exist gcloud compute routers nats describe $CLUSTER-nat-gw --router=$CLUSTER-router --region=REGION --project=$PROJECT 2>/dev/null \ && gcloud compute routers nats delete $CLUSTER-nat-gw --router=$CLUSTER-router --region=REGION --project=$PROJECT --quiet gcloud compute routers describe $CLUSTER-router --region=REGION --project=$PROJECT 2>/dev/null \ && gcloud compute routers delete $CLUSTER-router --region=REGION --project=$PROJECT --quiet # Delete any remaining custom routes gcloud compute routes list --project=$PROJECT --filter="network:$CLUSTER" --format="value(name)" 2>/dev/null | \ while read route; do gcloud compute routes delete --project=$PROJECT --quiet $route 2>/dev/null || true; done # Delete the subnet and network if they still exist gcloud compute networks subnets describe $CLUSTER --region=REGION --project=$PROJECT 2>/dev/null \ && gcloud compute networks subnets delete $CLUSTER --region=REGION --project=$PROJECT --quiet gcloud compute networks describe $CLUSTER --project $PROJECT 2> /dev/null \ && gcloud compute networks delete $CLUSTER --project $PROJECT --quiet
11. 恭喜
恭喜您完成本程式碼研究室。
涵蓋內容
- 如何建立及準備 GCE VM,以供 AlloyDB Omni 使用。
- 如何安裝及執行 AlloyDB Omni RPM 自動調度管理工具。
- 如何為高可用性參考架構安裝及設定 AlloyDB Omni RPM。
如要進一步瞭解 AlloyDB Omni,請參閱說明文件。